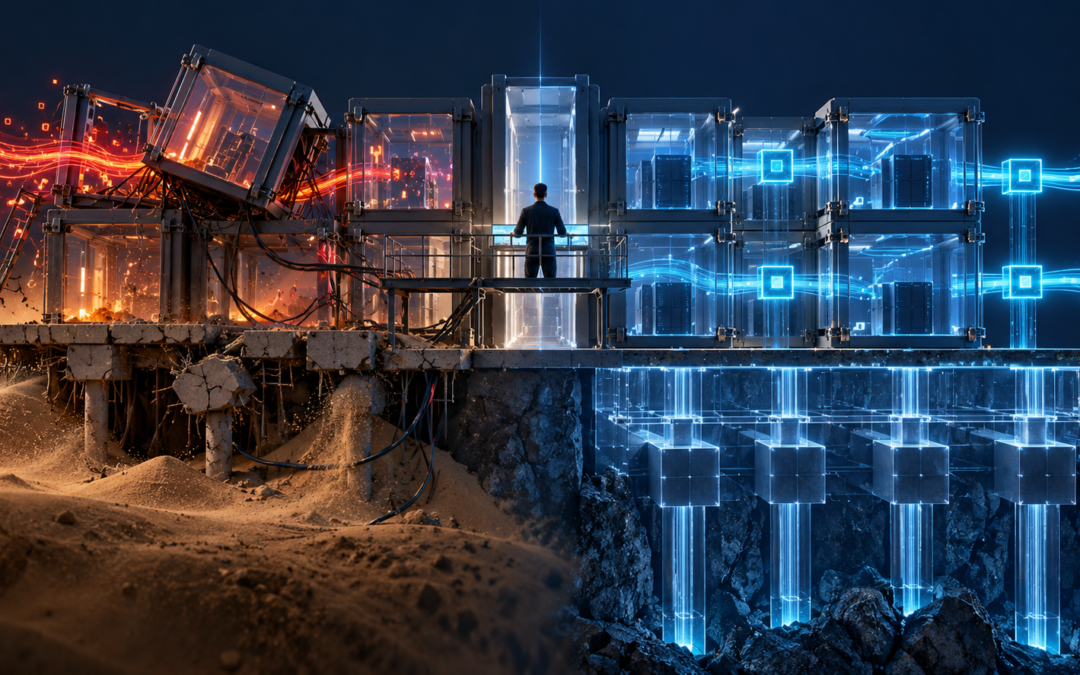
In the rush not to be left behind, many companies build AI on foundations of sand. The first layer looks solid: a model answers correctly, a demo impresses the room, and the project reaches production. Underneath, however, costs are not measured, data ownership is unclear, and no one can reconstruct why the system made a particular decision. The debt is already there. It simply has not sent its invoice yet.
AI governance belongs in the architecture from the beginning. Its purpose is not to slow innovation, but to prevent a promising experiment from becoming a system that must be rebuilt under pressure. In that sense, governance is technical insurance: it protects the company’s freedom to evolve and the long-term profitability that depends on it.
The Invisible Cost of Technical Debt in AI
Governance becomes easier to justify when technical debt is understood as a delayed operational cost. Imagine an AI assistant launched quickly through an external API. There are no spending limits, its data has grown without structure, and the system keeps no usable record of how its decisions are produced. For a while, none of this appears to matter. The assistant works and adoption grows.
Then usage increases. API costs become unpredictable, responses lose consistency, and an audit reveals that no one can explain a disputed answer. At that point, the team is rebuilding the foundations while the building is already occupied. The company pays twice: first for the speed of the launch, and then for the controls that should have been part of the design.
The Three Pillars of AI Governance
Governance fails when it lives only in policy documents. It has to become part of the system, visible in access rules, audit trails, cost controls and the tools employees are actually allowed to use. In practice, three areas carry most of the weight:
Compliance and Risk Control: Data cannot be treated as harmless input. Teams need to know where it came from, who can use it, which decisions require human review and what evidence will remain if a decision is challenged. The NIST AI Risk Management Framework provides a useful reference for organizing these responsibilities throughout the AI lifecycle.An architecture that cannot answer those questions becomes fragile the moment scrutiny arrives.
Performance and Cost Monitoring: An AI system can remain technically available while becoming economically unusable. Governance therefore needs visibility into usage, latency, model quality and cost per interaction. The purpose is not to accumulate dashboards. It is to detect when the system is drifting away from the value it was built to create.
Shadow AI Management: Employees will use external AI tools when the official alternatives are too slow, too limited or simply absent. Prohibition alone rarely solves the problem. The safer response is to provide approved tools that are useful enough to compete with unofficial alternatives, while keeping sensitive data within clear boundaries.
Avoiding Constant Architectural Redesign
Architecture rarely fails in one dramatic moment. More often, it accumulates exceptions: a prompt tied to one provider, a data pipeline designed for one model, business rules hidden inside application code, or monitoring added only after the first incident. Each shortcut makes the next change more difficult, until replacing a model or introducing a new control means touching the entire system.
Governance reduces this coupling by defining stable boundaries around data, models, prompts, policies, evaluation and observability. When those boundaries exist, a team can replace a model, tighten access rules or introduce a more efficient provider without redesigning the product around it. Modularity is not elegance for its own sake. It is how a company keeps its future decisions open.
Governance as a Trust Engine
Trust is not created by declaring an AI system responsible. It is earned when the organization can explain who controls the data, how performance is monitored, what happens when the model is wrong and who has the authority to stop it. Those answers matter to regulators and clients, but also to the engineers expected to keep the system running when something goes wrong.
Teams move faster when these boundaries are clear. They can experiment without guessing which data may be used, release changes without losing traceability and correct failures without searching through an opaque chain of decisions. Governance removes uncertainty from the parts of innovation that should never depend on improvisation.
AI governance is therefore part of what makes the architecture an asset. The real question is not whether the AI works today, but whether the company will still understand it, control it and afford it when the system becomes important.