In a microservices system, complexity does not disappear. It moves. Without a clear entry point, every client must understand how services are organized, which version to call, how to authenticate, and what to do when part of the system is unavailable. That knowledge quickly leaks into mobile applications, web interfaces, and partner integrations.
An API Gateway for microservices creates a deliberate boundary between clients and internal services. It can centralize routing, authentication, rate limits, protocol translation, and observability. But centralization also concentrates responsibility. A poorly designed gateway can become a bottleneck, a single point of failure, or a place where too much business logic accumulates.
The architectural question is therefore not simply whether to use an API Gateway. It is which complexity should be absorbed at the edge, which should remain inside the services, and whether the operational cost of the gateway is justified by the system behind it.
What an API Gateway for Microservices Actually Does
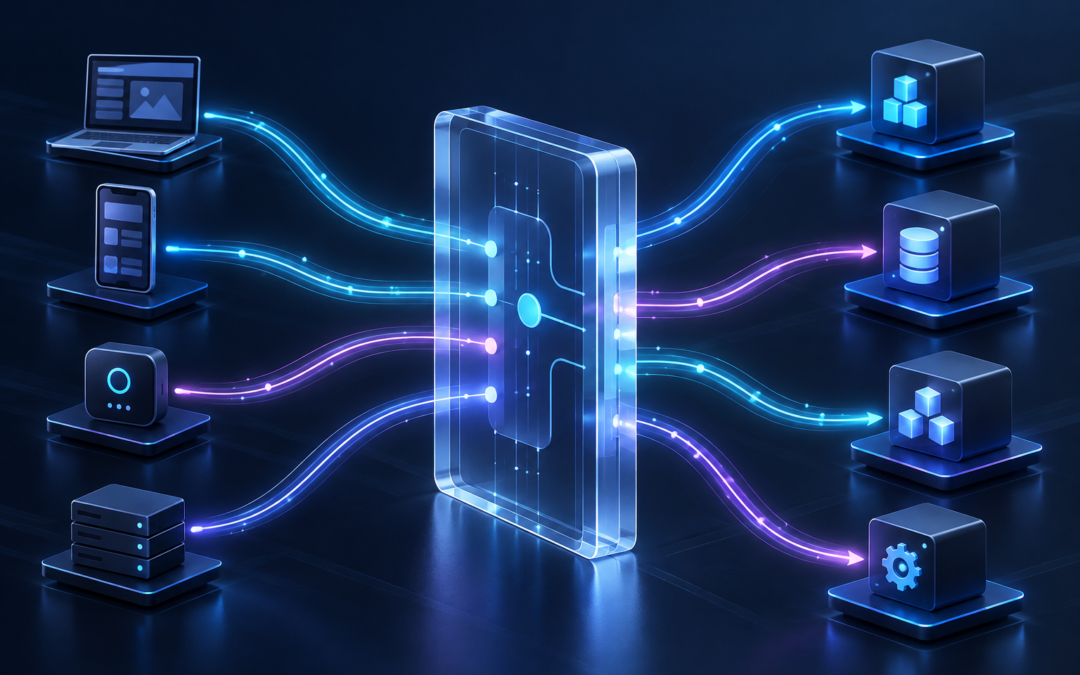
An API Gateway is a controlled entry point through which client traffic reaches internal services. Instead of requiring every client to know the location, protocol, version, and security rules of each service, the gateway translates a public request into the internal interactions needed to fulfil it.
Its value is not that it removes complexity. It prevents the same complexity from being reproduced across mobile applications, web interfaces, connected devices, and partner integrations. It also allows internal services to evolve without exposing every structural change to their consumers.
This is the purpose of the API Gateway pattern: to give clients a stable entry point while allowing the internal structure of the system to evolve.
Its main responsibilities generally fall into four areas:
- Traffic control: Routing requests to the appropriate services and, when necessary, combining several service responses into one client-facing result.
- Security and protection: Applying authentication, authorization, rate limits, and other shared policies before traffic reaches internal services.
- Translation and performance: Adapting protocols or data formats and caching suitable responses when doing so is safe and useful.
- Visibility and consistency: Producing common logs, metrics, traces, and error responses across the system.
The boundary matters. Shared concerns that apply to incoming traffic belong naturally at the gateway. Business rules and domain decisions should remain inside the services that own them. When that distinction is ignored, the gateway can gradually become another monolith.
When an API Gateway Earns Its Complexity
An API Gateway is not free infrastructure. It introduces another component to deploy, secure, monitor, scale, and recover when something goes wrong. It is justified when the complexity it removes from clients and services is greater than the complexity it adds to the platform.
Because it sits directly on the request path, its design must also prevent downstream failures from spreading across the system, which is where patterns such as the circuit breaker become relevant.
When It Adds Real Value
An API Gateway becomes useful when several clients or services need to evolve independently while continuing to communicate through a stable external contract. It is particularly valuable when the system needs:
- Shared protection at the edge: Authentication, authorization, rate limiting, and traffic policies can be applied consistently before requests reach internal services.
- A stable interface over changing services: Internal services can be moved, divided, replaced, or versioned without forcing every client to understand the new topology.
- Request aggregation or transformation: A single client request may require data from several services or translation between different protocols and formats.
- Consistent observability: Logs, traces, latency measurements, and failure patterns can be captured at a common entry point.
- Different experiences for different clients: Web, mobile, connected devices, and partner systems may need different representations of the same underlying capabilities.
Traffic volume alone is not a sufficient reason to introduce a gateway. The stronger reason is the need to control a boundary shared by multiple consumers and services.
When It May Add More Than It Solves
A gateway may be unnecessary when a system has one client, one relatively simple backend, and few shared policies. In that situation, a reverse proxy, load balancer, or existing cloud service may already provide everything the application needs.
The decision should also reflect the team’s operational capacity. A gateway that nobody can observe, scale, or recover confidently can reduce reliability instead of improving it. The same is true when business logic begins to accumulate at the edge and every change requires modifying the gateway.
A monolithic application does not automatically rule out an API Gateway, just as a microservices architecture does not automatically require one. The decision depends on the boundary that must be controlled, not on the architectural label attached to the system.
How to Choose an API Gateway Implementation
Choosing an API Gateway is not primarily a comparison of feature lists. The more important questions are where the gateway will run, who will operate it, how much control the team needs, and what should happen when it becomes unavailable.
Managed Cloud Gateways
Services such as Amazon API Gateway, Azure API Management, and Google Cloud’s Apigee reduce the infrastructure that a team must operate directly. They provide capabilities such as traffic management, security policies, monitoring, and integration with the provider’s wider cloud ecosystem.
This approach is attractive when the system already relies heavily on one cloud platform and the team prefers to buy operational capacity rather than build it. The trade-off is greater dependency on the provider’s pricing, deployment model, limits, and surrounding services.
Dedicated Gateway Platforms
Platforms such as Kong and Tyk offer more control over deployment and can support self-managed, hybrid, or multi-cloud environments. Their plugin ecosystems and configuration models allow teams to adapt the gateway to more specific architectural requirements.
That flexibility does not remove operational responsibility. The team must still manage capacity, upgrades, configuration, security, observability, and recovery. A self-managed gateway only creates independence when the organization is prepared to operate it reliably.
Framework-Based Gateways
A framework such as Spring Cloud Gateway can be a natural choice for teams already working within the Spring ecosystem. It allows the gateway to follow familiar development, testing, and deployment practices.
The apparent simplicity can be misleading. The gateway remains a production application, and every customization becomes code that must be maintained. This approach works best when the required behaviour is specific enough to justify development but not so unusual that an entirely custom gateway is necessary.
A Custom Gateway
Building a gateway from the ground up offers the greatest control, but it also transfers every responsibility to the development team. Routing, security, resilience, protocol handling, observability, scaling, and failure recovery all become part of the product that the organization must maintain.
A custom implementation should therefore answer a genuine constraint that existing products cannot satisfy. Control alone is not a sufficient reason. If the differentiating requirement cannot be stated clearly, the organization is probably rebuilding infrastructure rather than creating business value.
The final decision should consider deployment constraints, expected traffic, latency requirements, security and governance, operational skills, failure recovery, total cost, and the risk of provider dependency. The best gateway is not the one with the longest feature list. It is the one whose responsibilities the team can understand and operate over time.
An API Gateway Is a Boundary, Not a Shortcut
An API Gateway can prevent the internal complexity of a microservices system from leaking into every client. It creates a place to control traffic, enforce shared policies, and preserve a stable external contract while the services behind it continue to evolve. That concentration of responsibility also makes it critical infrastructure.
The objective is not to place every concern in the gateway. It is to establish a clear boundary: shared concerns related to incoming traffic belong at the edge, while business rules and domain decisions remain inside the services that own them. When the gateway begins making those decisions, its initial convenience gradually turns into architectural coupling.
Used deliberately, an API Gateway for microservices allows a system to change without forcing every consumer to change with it. Introduced by habit, it can become another bottleneck that the organization must work around. Its architectural value therefore depends as much on what it is designed not to do as on the capabilities it provides.